Building Trustworthy AI - LP background
ReversingLabs
High-volume & large-file threat detection

Scalable File Analysis

Analyze every file moving through your enterprise, any type and any size, and get verified malware verdicts in real time.

Trusted by the Fortune 500 and leading cybersecurity vendors.

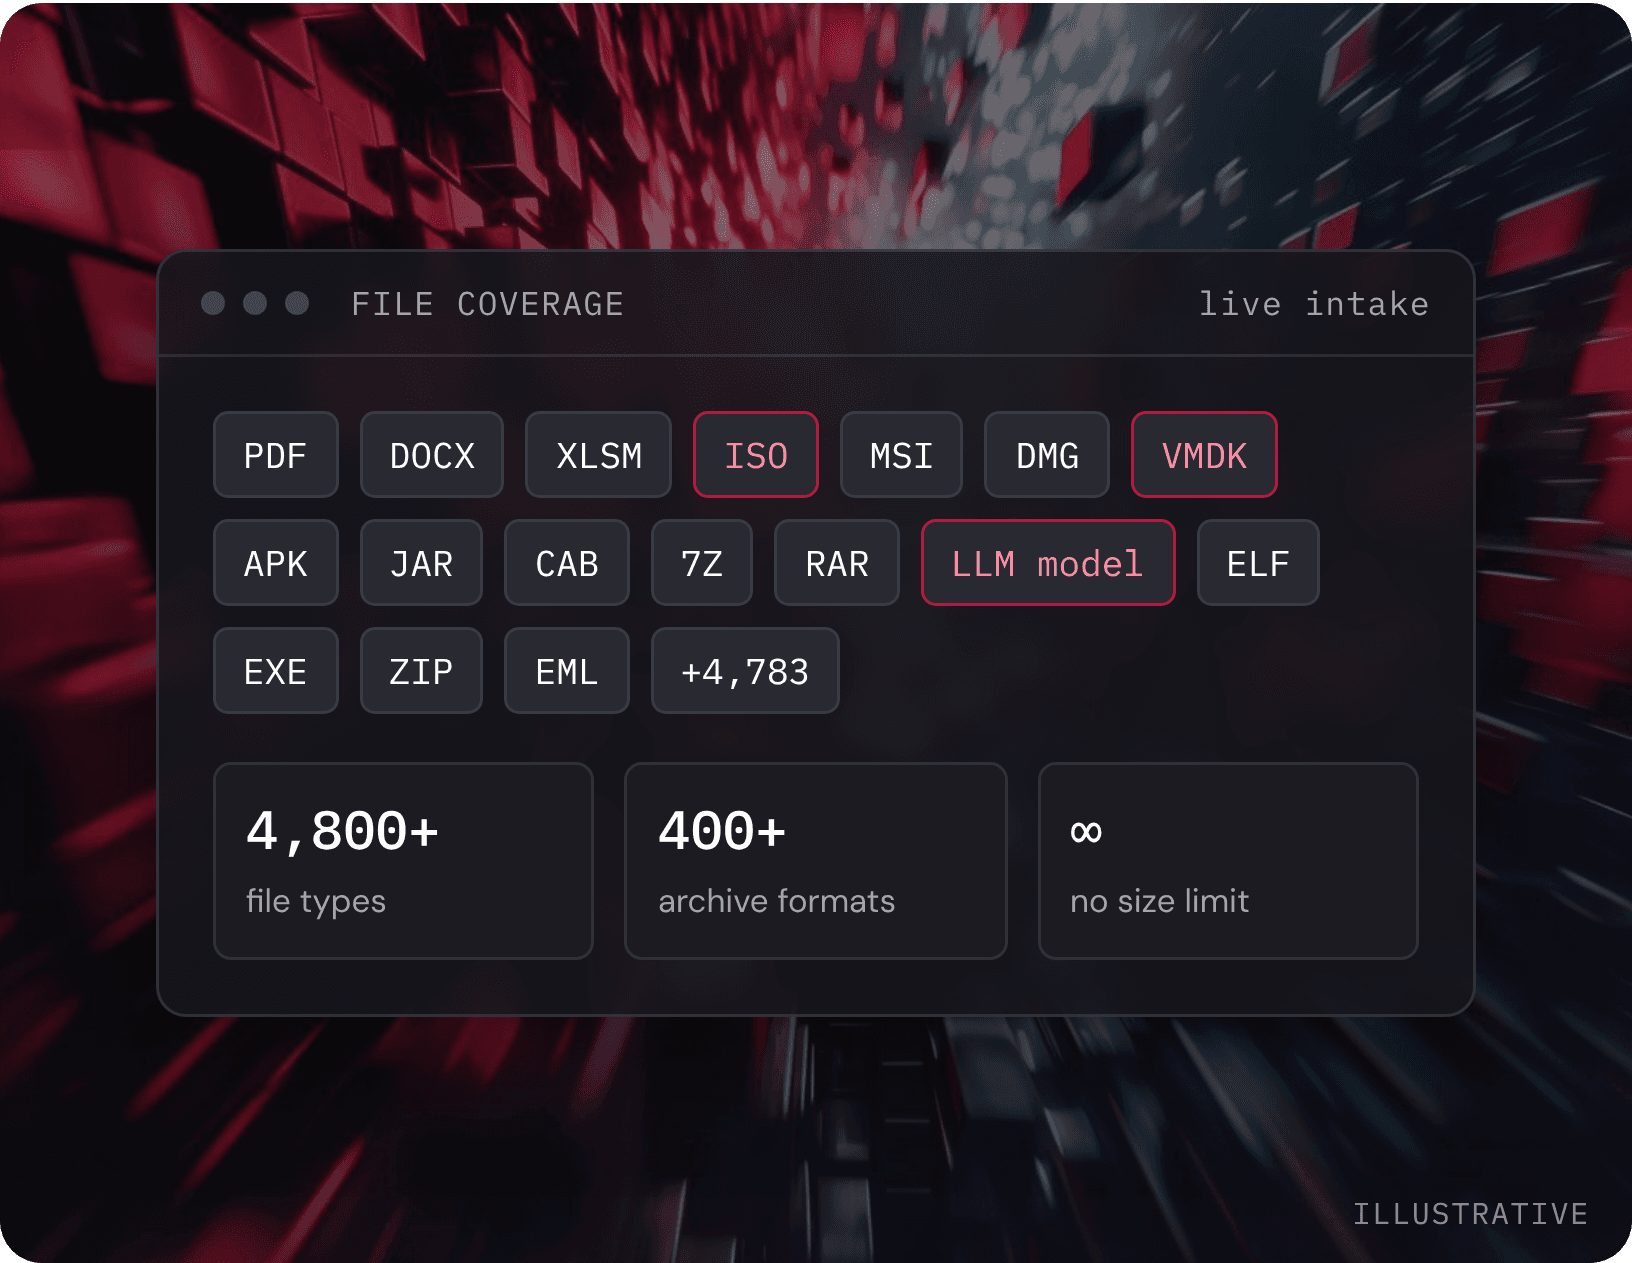
4,800+

file types analyzed

Any size

no file size limitations

How ReversingLabs closes the gap

Visibility, detection and scale in one file analysis platform.

Most tools stop at the file size limit, the archive wrapper or the queue. ReversingLabs keeps going.

See inside every file: any type, any size.

Analyze 4,800+ file types and unpack 400+ archive formats with no file size limits, so nothing gets through just because it's too big or too complex to scan.

  • Covers ISOs, CABs, installers, VMDKs and LLM models
  • Out-of-the-box connectors for email, cloud storage, network shares and collaboration tools
  • Processes millions of objects automatically, with no manual triage

Catch the malware your perimeter misses.

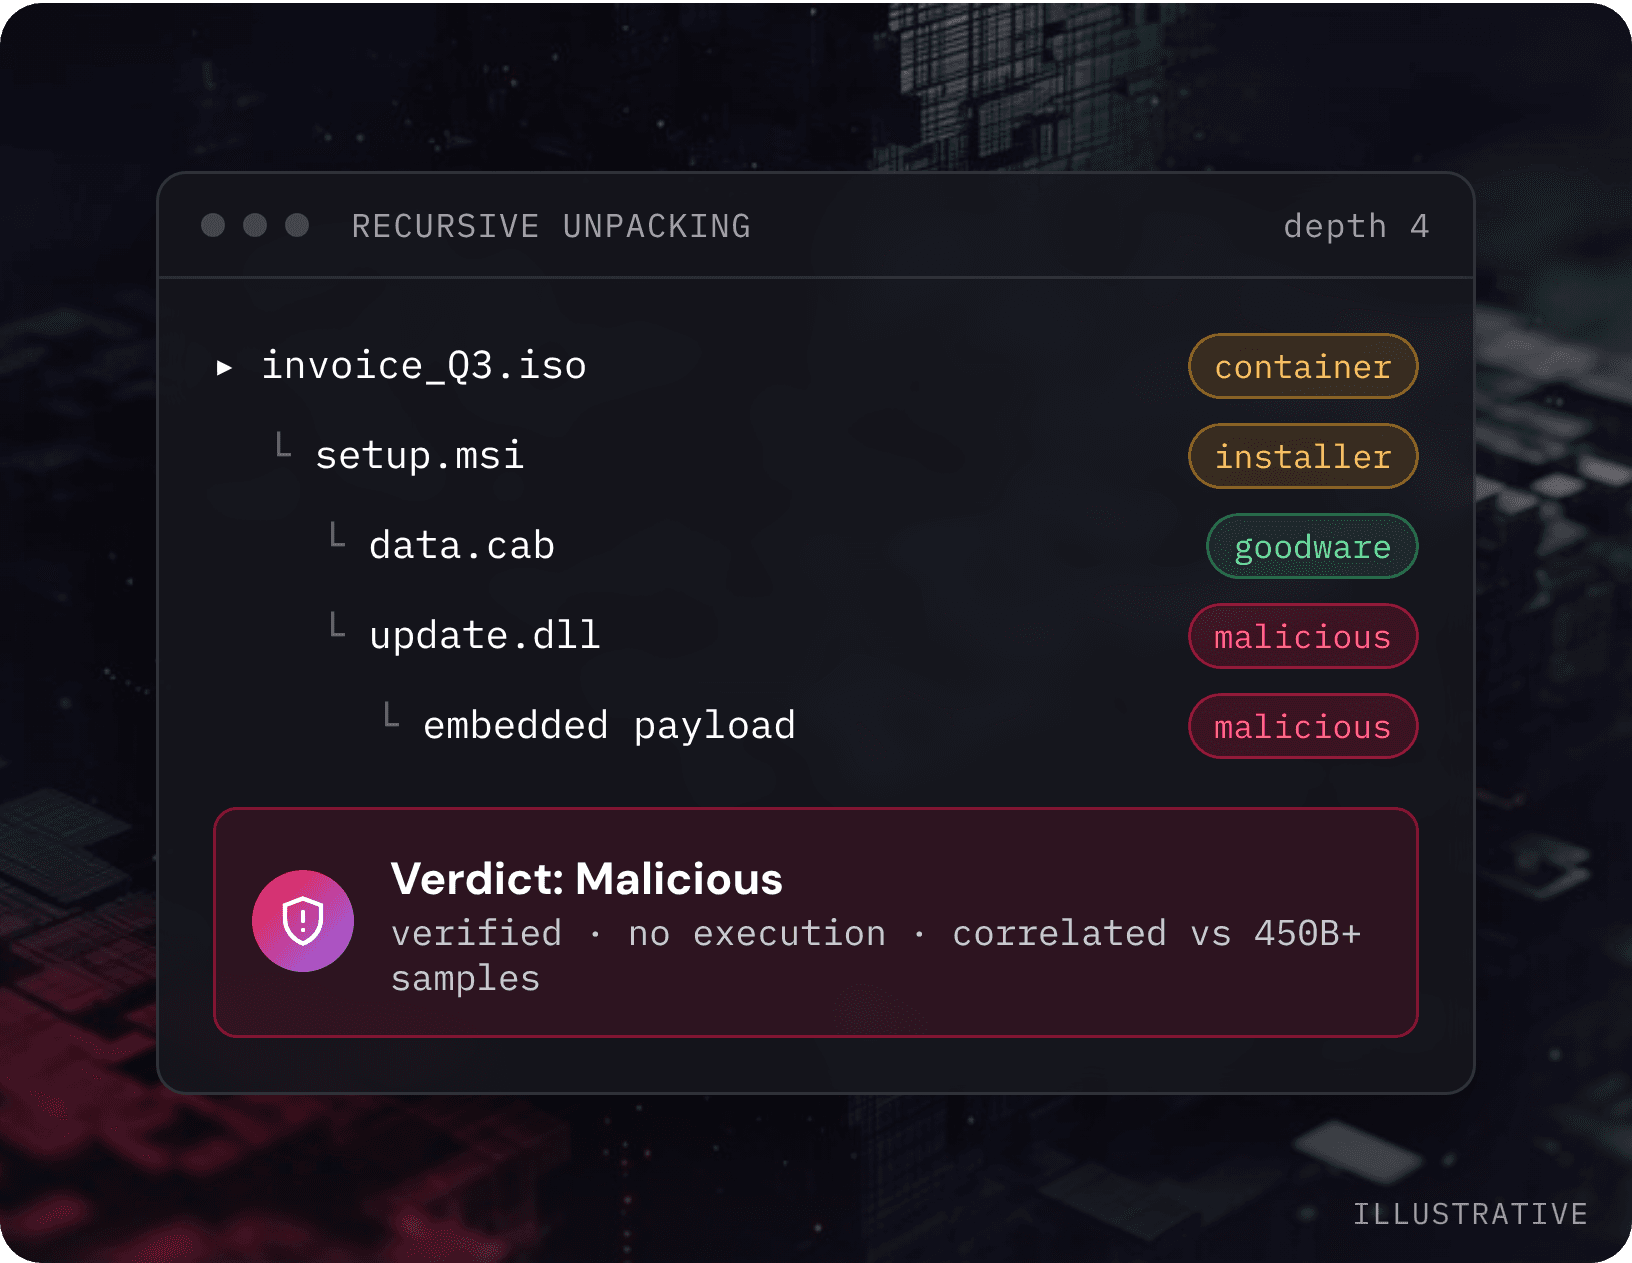
AI-driven binary analysis deconstructs each file, recursively unpacks every layer and checks what it finds against 450B+ known malware and goodware samples.

  • Static analysis: no execution or sandbox detonation required
  • Extracts metadata and embedded objects from every nested layer
  • Final, verified verdicts instead of a score to interpret

Scale to millions of files without slowing the SOC.

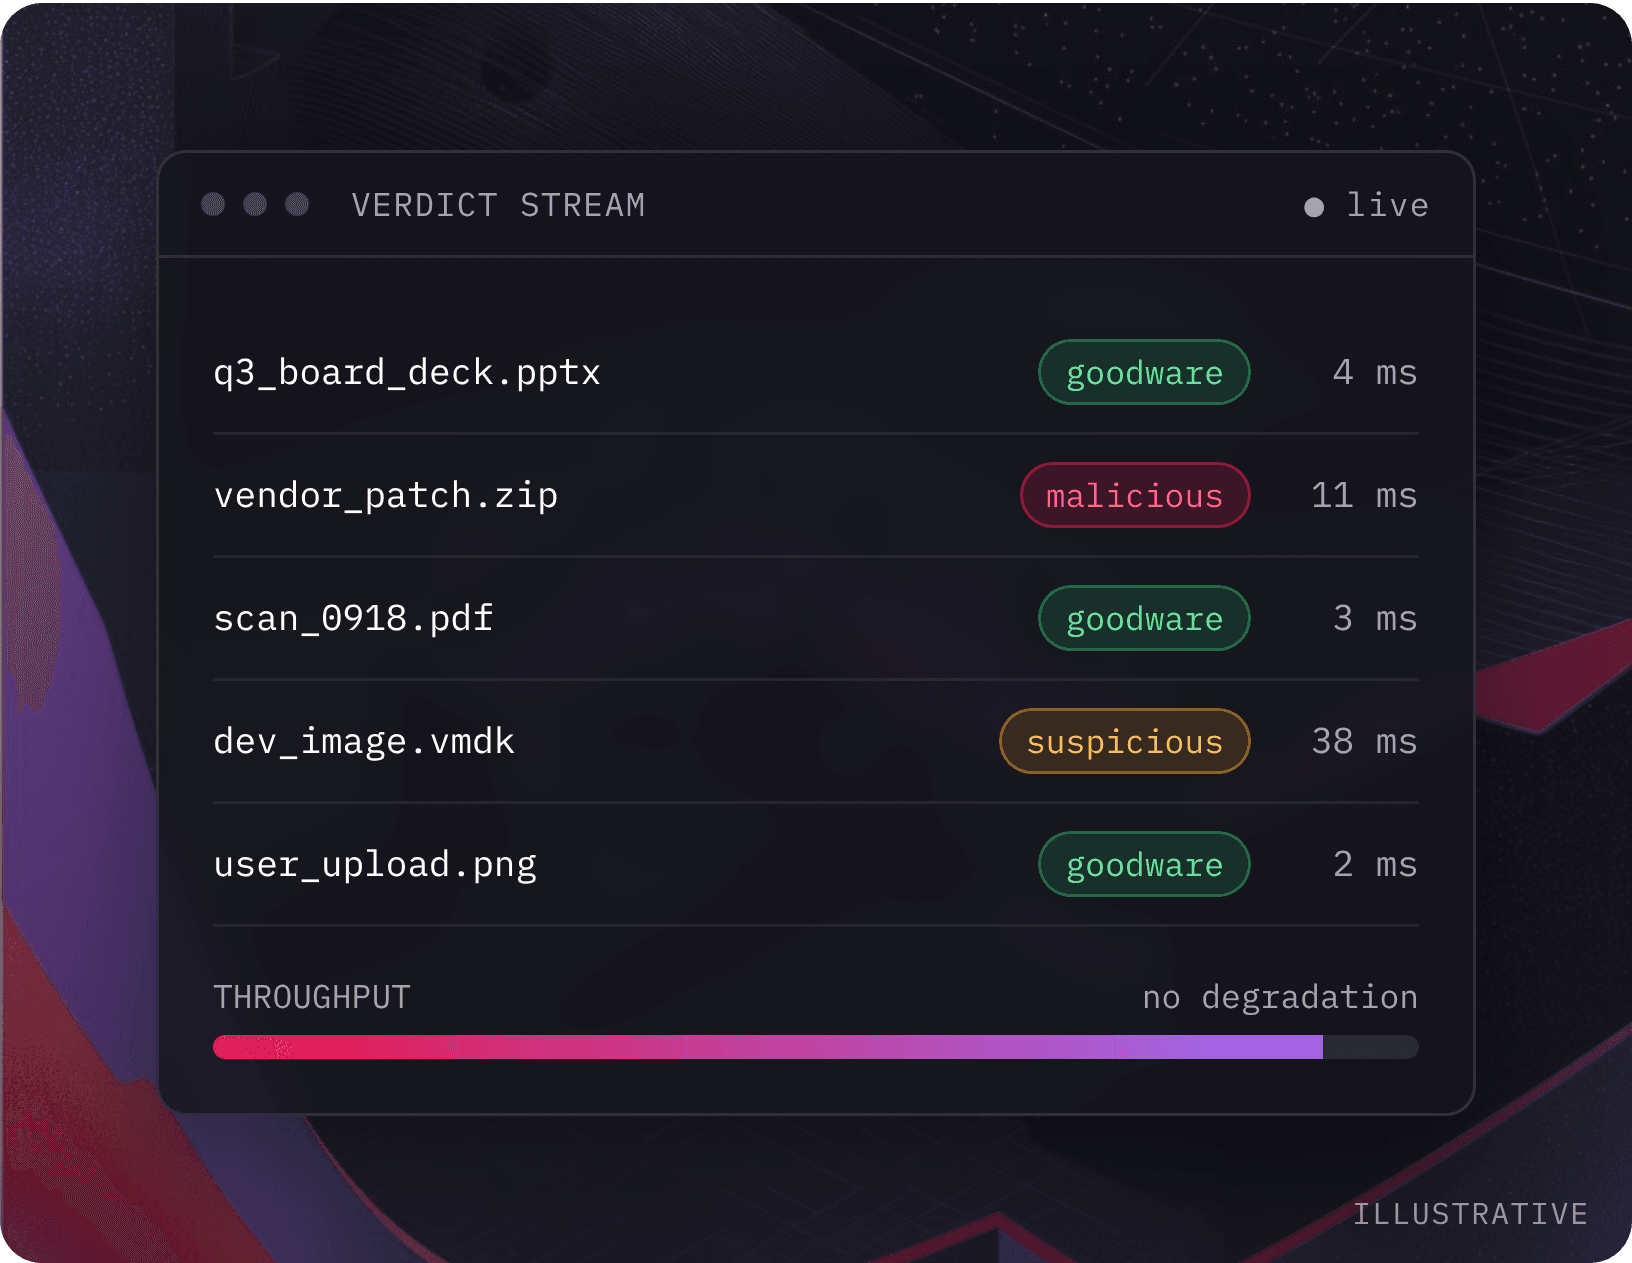
A high-throughput engine classifies files in real time at enterprise volume and sends verdicts to the SIEM, SOAR and TIP tools your analysts already use.

  • Millions of files assessed without performance degradation
  • Millisecond time to result through the API
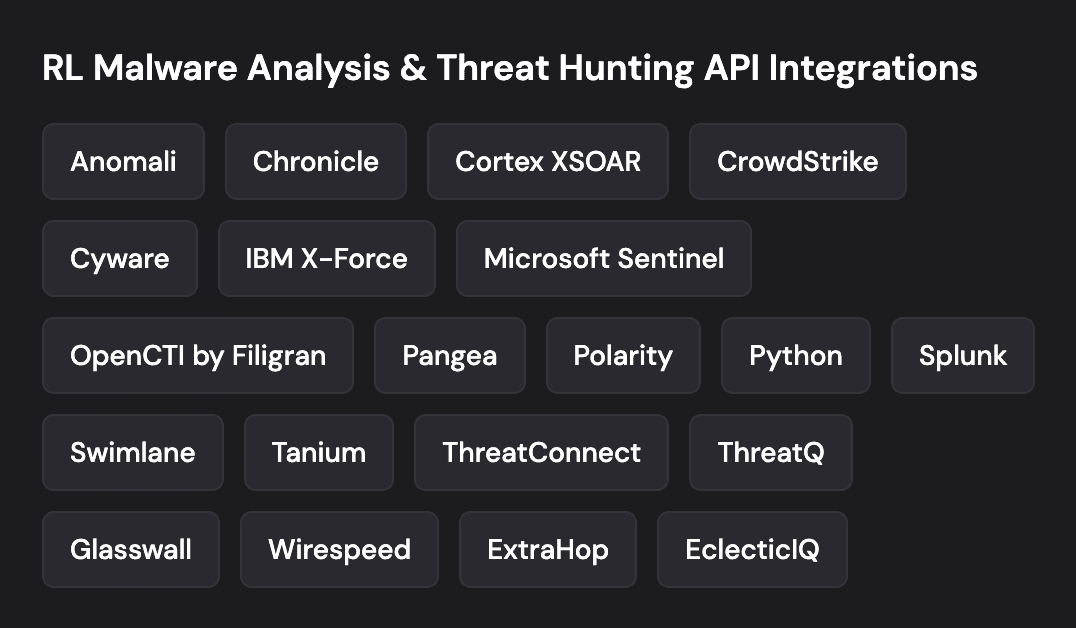
  • 20+ integrations, including Splunk, Microsoft Sentinel, Cortex XSOAR and CrowdStrike

Verdicts where your analysts already work.

Add trusted file intelligence and deep malware insight to the enterprise platforms you already run, with no new console to learn.

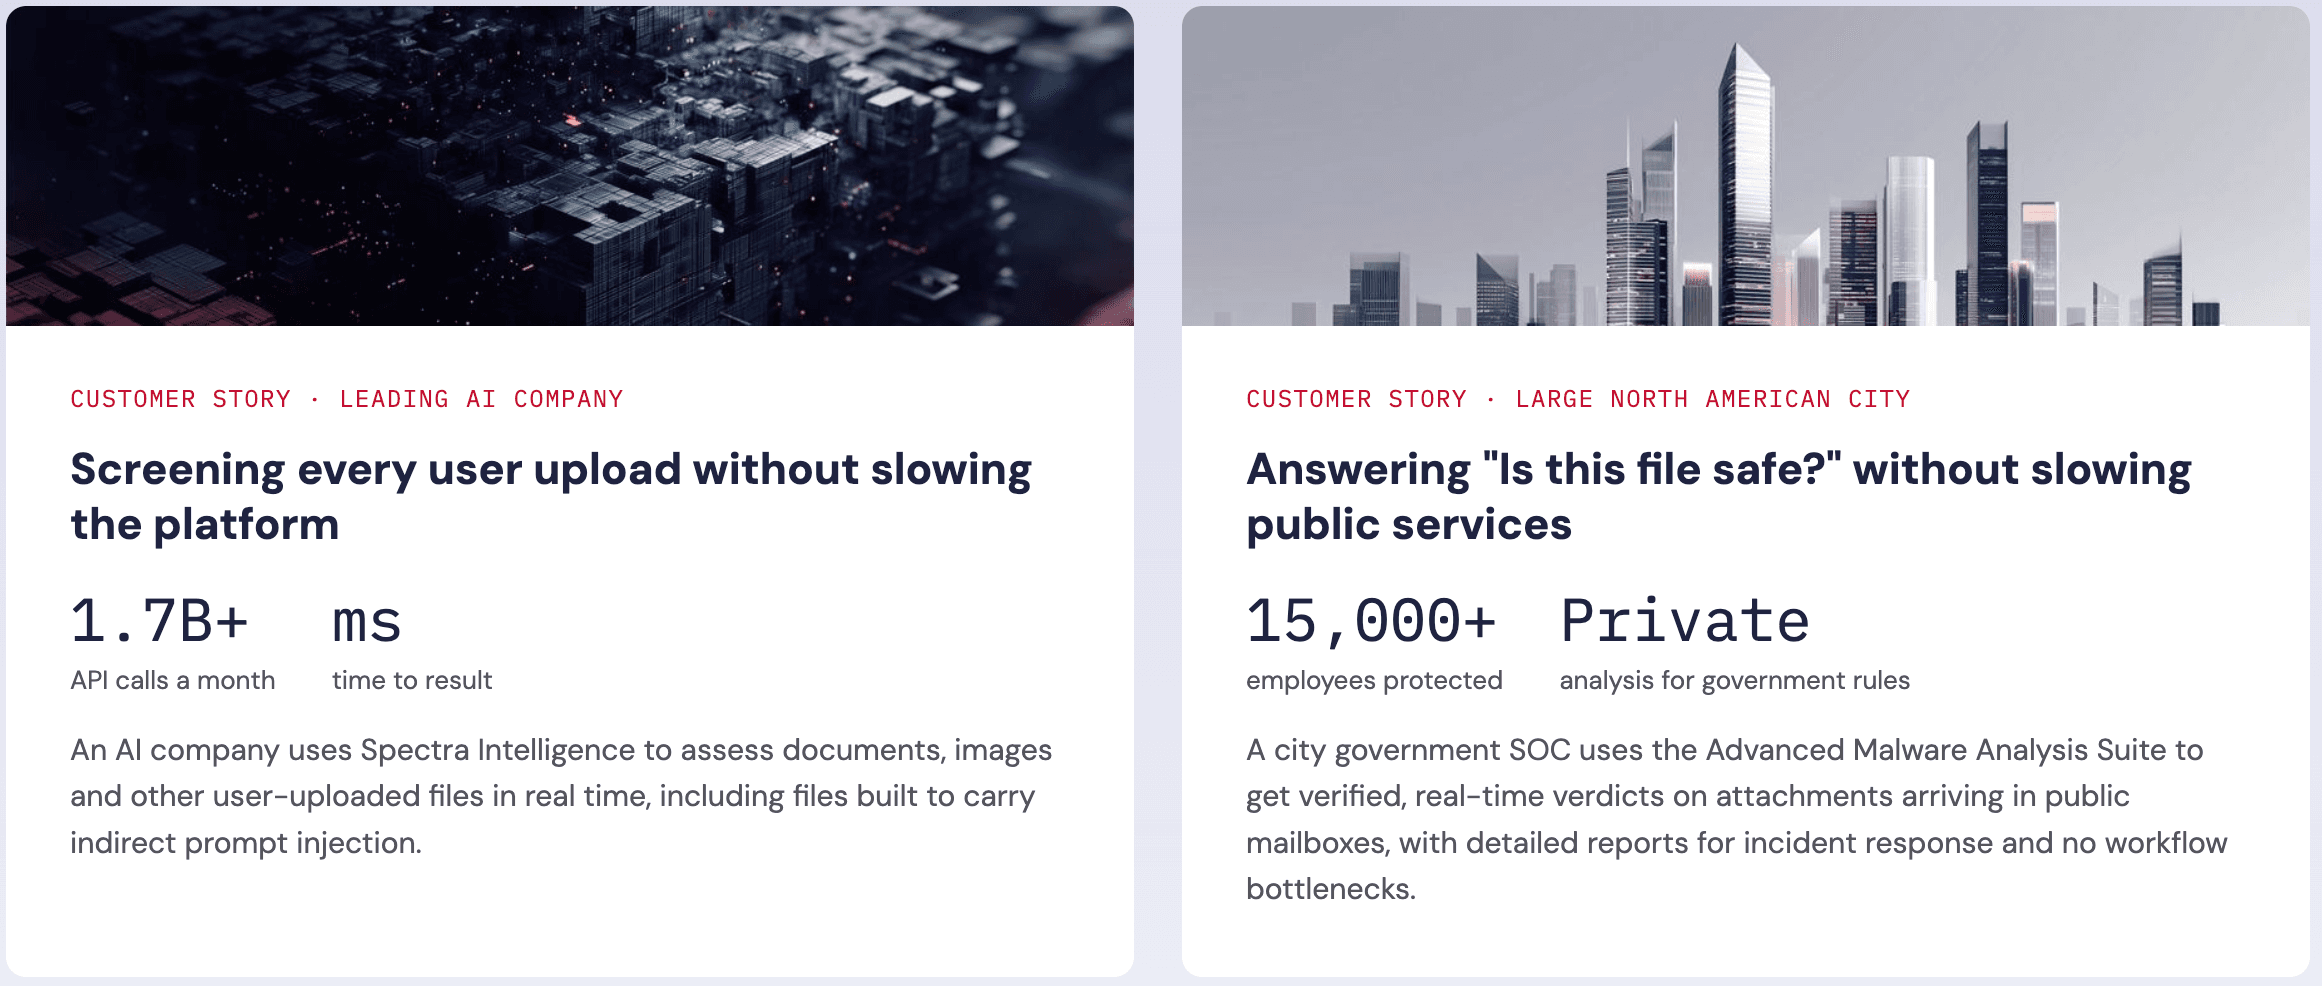
Proven at enterprise scale

FAQ

Scalable file analysis is the ability to inspect every file entering or moving through an organization, at any volume and size, and return a reliable malware verdict without creating a bottleneck for security operations.

ReversingLabs analyzes more than 4,800 file types and unpacks more than 400 archive formats, including large, complex objects such as ISOs, installers, VMDKs and LLM models.

No. ReversingLabs uses AI-driven static binary analysis to deconstruct files without executing them. It recursively unpacks every layer and correlates the results against more than 450 billion malware and goodware samples.

Its high-throughput processing engine assesses millions of files without performance degradation and returns results in milliseconds through APIs and out-of-the-box integrations.

Integrations include Splunk, Microsoft Sentinel, Chronicle, Cortex XSOAR, CrowdStrike, Tanium, ThreatConnect, ThreatQ, Anomali, Swimlane and more.

Ready to close the malware visibility gap?

See how ReversingLabs analyzes your file volume, at your scale.

Book a Demo

Millions

of files assessed without performance degradation

450B+

sample corpus of files, malware and threats
01_visibility_image_3x
02_detection_image_3x
03_scale_image_3x
01_NVIDIA_black_xs_pad
02_Google_black_xs_pad
03_Microsoft_black_xs_pad
04_Amazon_black_xs_pad
05_Broadcom_black_xs_pad
06_Walmart_black_xs_pad
07_JPMorgan_Chase_black_xs_pad
RL Malware Analysis & Threat Hunting API Integrations
01_visibility_label_transparent
02_detection_label_CMS_width
03_scale_label_CMS_width
Proven at enterprise scale
reversinglabsReversingLabs: Home
Privacy PolicyCookiesImpressum
All rights reserved ReversingLabs © 2026
XX / TwitterLinkedInLinkedInFacebookFacebook
Instagram
Instagram
YouTubeYouTube
blueskyBluesky
RSSRSS
Back to Top
01_visibility_standout_innovation_white.png
02_detection_standout_innovation_white
03_scale_standout_innovation_white