Inspect opaque software
Decompose binaries, containers, installers, firmware, and other complex artifacts that can hide risk beyond network behavior alone.
ExtraHop RevealX identifies suspicious network activity, while ReversingLabs adds the file and software intelligence needed to determine what is actually moving through the environment, whether it can be trusted, and how teams should respond.
ReversingLabs adds deep file and software intelligence to those investigations, helping security teams analyze binaries, packages, and other artifacts for malware, tampering, hidden functionality, and other software risks.
Together, network visibility and file intelligence can help organizations move from detecting suspicious activity to understanding the artifacts behind it, accelerating threat hunting, improving investigations, and supporting more confident response.
RevealX tells security teams what is moving across the network. ReversingLabs adds the evidence inside the files, packages, and binaries - giving analysts a faster path from suspicious activity to a confident verdict.
Decompose binaries, containers, installers, firmware, and other complex artifacts that can hide risk beyond network behavior alone.
Pivot from a RevealX indicator or carved file to malware family, reputation, behavior, and supporting evidence in seconds.
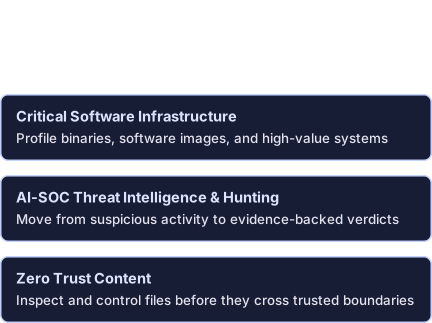
Apply positive-security controls to the files entering sensitive environments, allowing known-good content and quarantining everything else.
Use the same ReversingLabs intelligence layer across infrastructure monitoring, threat hunting, and content controls - without replacing the ExtraHop workflows your teams already use.
powered by Spectra Assure
Start with binary images, VMs, containers, or firmware associated with critical systems.
Decompose the full software package to establish a trusted baseline and expose hidden risk.
Feed findings back into ExtraHop context, triggers, and response workflows.
powered by Spectra Intelligence + Analyze
Launch a hunt from curated feeds, private intelligence, or a suspicious network indicator.
powered by Spectra Detect
Inspect uploads, transfers, and file movement across high-value boundaries.
Identify format, recursively unpack content, and check reputation and malware behavior.
BETTER TOGETHER
ExtraHop RevealX gives defenders high-fidelity visibility into what is happening across the network. ReversingLabs adds deep file and software intelligence so teams can understand the artifacts
behind that activity - before they execute, while analysts investigate, and when enforcement matters.
The result is a stronger detection loop: network activity creates the signal, file intelligence adds the verdict, and the combined evidence helps teams respond with greater speed and confidence.
Add the artifact-level context network detections alone cannot provide, while keeping analysts inside familiar RevealX workflows.
File Intelligence
Use reputation, prevalence, threat-actor attribution, and history drawn from a massive corpus of analyzed files.
Formats Supported
Inspect complex file types and recursively unpack archives, installers, packages, firmware, containers, and more.
Fast Verdicts
Return high-confidence verdicts quickly enough to support hunting, triage, and machine-speed workflows.
Deploy Where Needed
Use hosted or private deployment options where control, residency, or sensitive content matters.
Metrics and deployment language reflect the source ExtraHop solution-page content provided for this concept.
START WITH THE PROOF OF VALUE
Scope a use case with your ExtraHop account team and see how artifact
intelligence strengthens network detection and response.
ExtraHop reveals suspicious network activity. ReversingLabs adds the file and software intelligence to determine what the artifact actually is - malicious, tampered, risky, or trusted - so teams can investigate faster and enforce with confidence.
Evaluate later versions or changes against what was previously approved.
ExtraHop records surface candidate hosts, files, and events for investigation.
Analyze the artifact and return malware behavior, family, reputation, and IOCs.
Return validated indicators and verdicts to RevealX and downstream controls.
Release approved content and isolate unknown or malicious files.
Send findings into ExtraHop for visibility, correlation, and response.

Here are the facts on Claude Mythos — and why a layered application security framework is essential.

The ML-BOM capability in RL's Spectra Assure SAFE Report provides immediate visibility into every ML model in your environment.