Spectra Assure Free Trial
Get your 14-day free trial of Spectra Assure for Software Supply Chain Security
Get Free TrialMore about Spectra Assure Free Trial
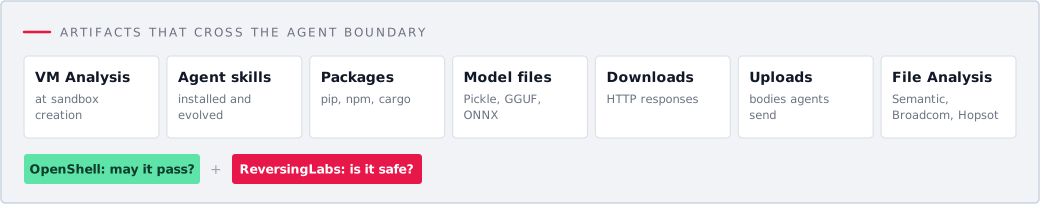
Autonomous agents download packages, install skills, load models, execute software, and move files as part of normal operation. Each artifact becomes part of the agent's effective attack surface.
NVIDIA OpenShell provides sandboxed execution and policy controls that govern what an agent is permitted to do and what resources it can access.
ReversingLabs adds intelligence about the software, packages, models, and files those agents interact with, giving security teams evidence about the artifacts entering and moving through agent workflows.
Together, policy and artifact intelligence can help organizations make more informed decisions before software is executed, while agents are operating, and when security teams investigate activity.
Analyze files, packages, models, and other artifacts before they’re trusted.
Admit only what has been analyzed
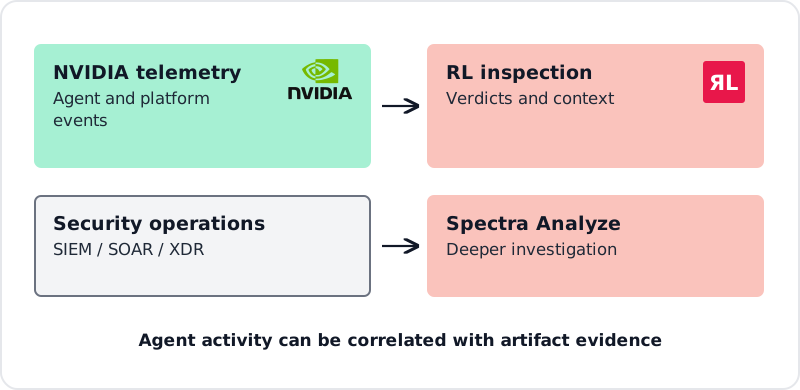
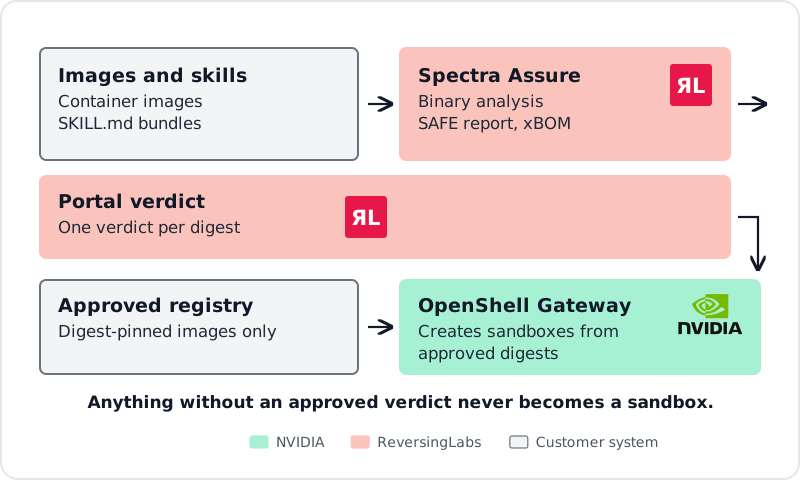
Spectra Assure analyzes every sandbox image and SKILL.md bundle at the binary level. Only approved digests reach the registry OpenShell builds sandboxes from, and a governance interceptor can make sure policy can't be quietly weakened later (pilot).
Pull only what has passed analysis
Packages and models come from your internal repository, gated by Spectra Assure and the Catalog add-on. Components that fail analysis never reach the sandbox, and the findings go to the team that requested them.
Inspect what agents send and receive
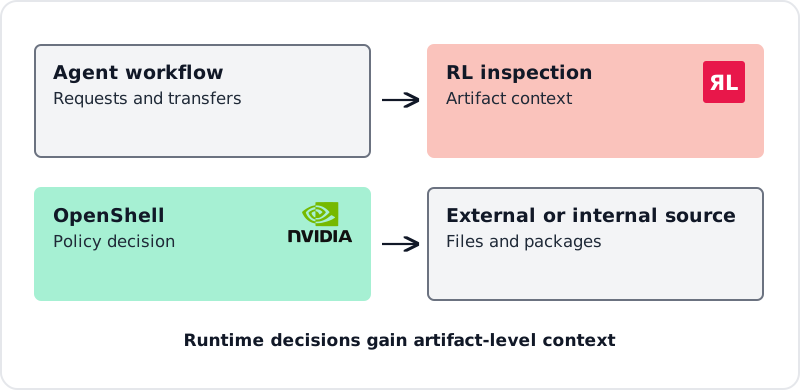
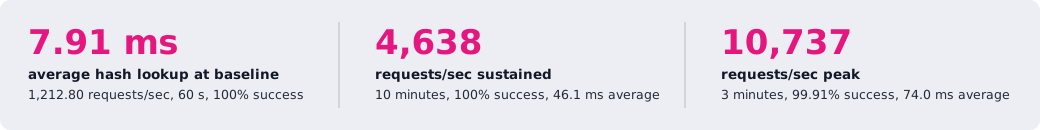
File Inspection Engine runs as OpenShell supervisor middleware. It checks outbound bodies before credentials are injected and, with OpenShell 0.1.x, downloads up to 4 MiB before the agent sees them. It is designed to resolve most requests by hash and file type in milliseconds.
Review what agents ask for
NVIDIA leaves the approval of new access to the organization. When a blocked agent proposes new network access, an RL reviewer checks the destination's reputation before the rule is approved, closing the gap NVIDIA documents for automatic approval of new public hosts.
Tap into one of the world's largest file reputation corpora to add context, history, and known-good / known-bad intelligence to every inspection.
NVIDIA built the runtime that decides what agents can do. Give it the evidence
to decide well. Talk to us about a pilot in your agent environment.
Uncover malware, tampering, and threats that traditional vulnerability scanning can miss.
Give AI agents deeper security context as they operate across enterprise environments.
Deliver fast hash lookups and selective deep inspection without slowing down agent workflows.
Turn hashes into verdicts
RL integration services turn Spectra Assure's approved hashes into the DOCA Argus allowlist, and every hash Argus reports from host memory gets a local verdict. Because containers are immutable, a warm cache answers most events without a lookup.
Investigate with evidence
OpenShell decisions, Argus telemetry, and RL verdicts converge in your SIEM with Spectra Intelligence reputation attached. Spectra Analyze gives responders the artifact-level story behind every deny.
Use fast hash lookups and selective deep inspection to support high-volume, machine-speed agent workflows.
Run inspection locally, in private environments, or across architectures where data residency and control matter.
Analyze 4,800+ file formats and recursively unpack complex files, packages, and models to expose what agents actually touch.

Here are the facts on Claude Mythos — and why a layered application security framework is essential.

The ML-BOM capability in RL's Spectra Assure SAFE Report provides immediate visibility into every ML model in your environment.