Spectra Assure Free Trial
Get your 14-day free trial of Spectra Assure for Software Supply Chain Security
Get Free TrialMore about Spectra Assure Free Trial
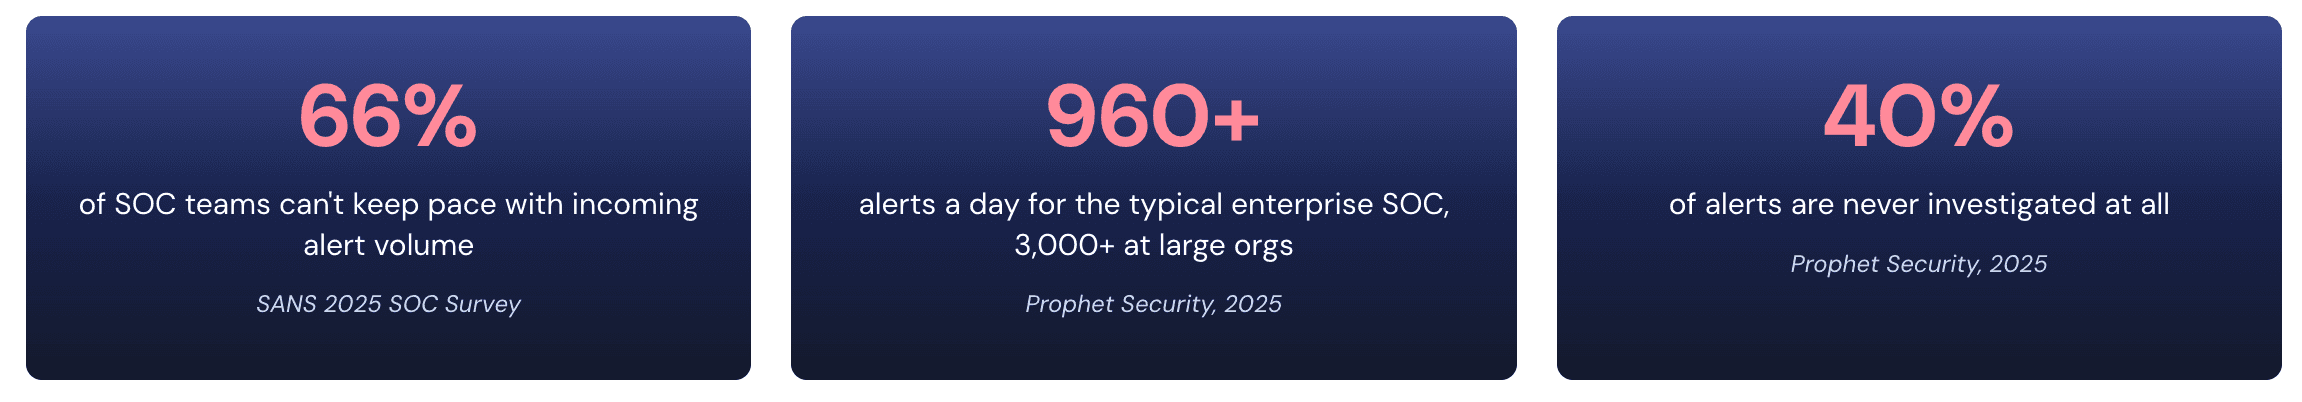
SOC teams are buried in alerts, and AI-driven attackers move faster than people can. Organizations are racing to deploy agentic SOC automation, only to discover that their agents are only as reliable as the data feeding them. Open-source intelligence and crowdsourced data like VirusTotal return sparse or conflicting signals on new or novel samples, resulting in agents either guessing or escalating everything back to a human. But the real risk is the alerts they close: a “clean” verdict built on thin data means a real threat is silently auto-closed.
An autonomous agent reasoning over incomplete, non-local, or stale intelligence doesn't accelerate response.
It automates bad decisions - at machine speed.
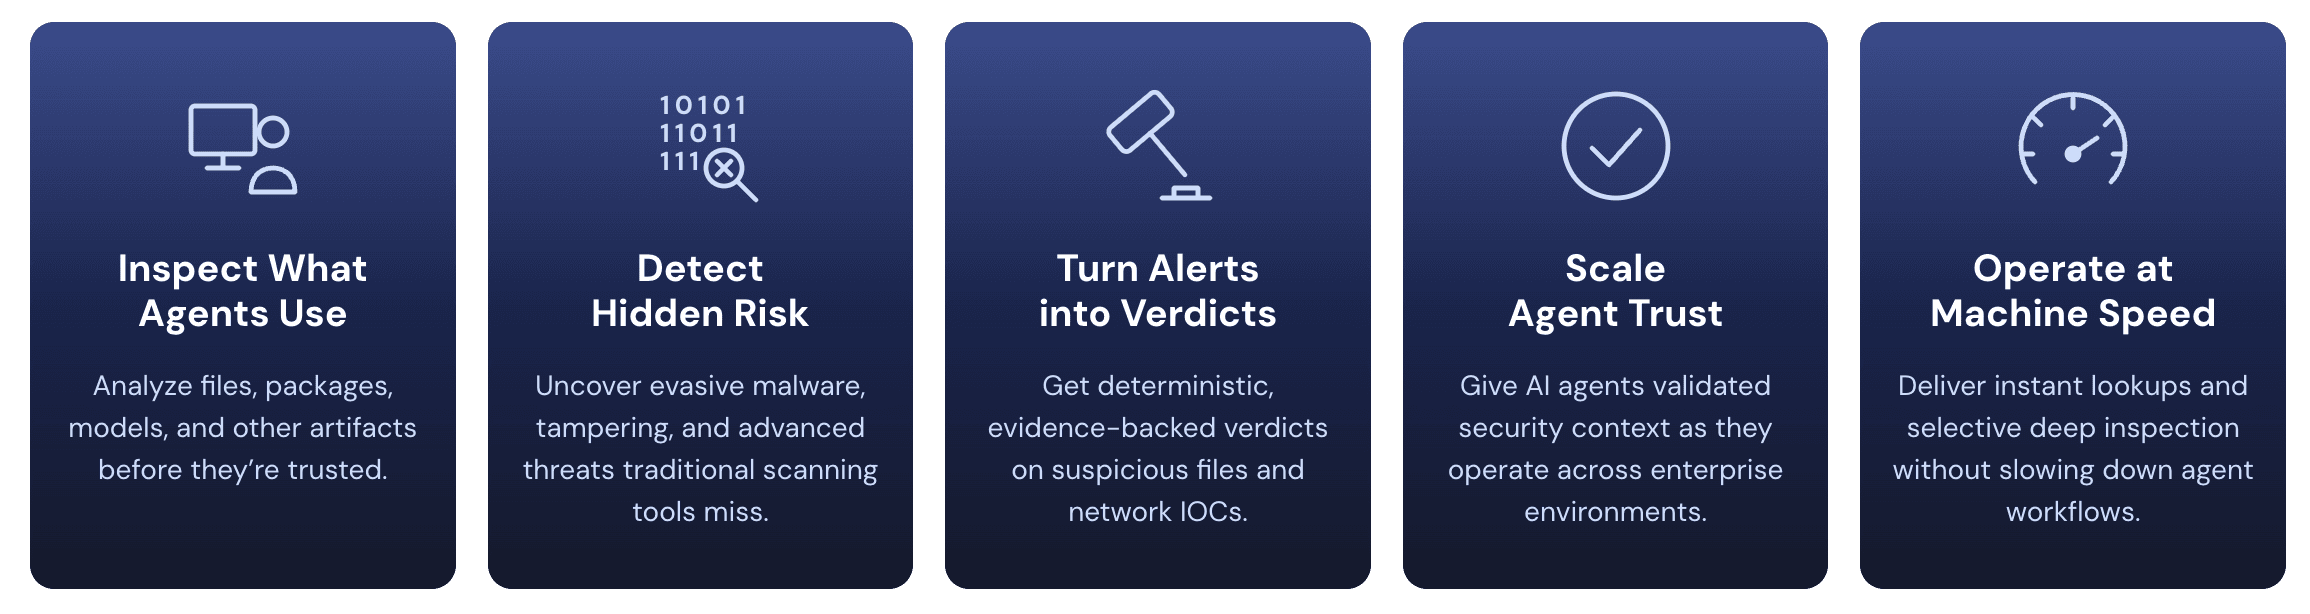
ReversingLabs for the Agentic SOC exposes RL's advanced malware analysis, real-time threat intelligence, and software supply chain analysis as APIs, connectors, skills, agents, and MCP Servers your agents call directly, on every file hash, network indicator, and software package. Each verdict comes from deconstructing the file or package itself, not from logs, identity, or network telemetry, and is checked against the industry's largest first-party corpus of over 450 billion analyzed files. The result is a deterministic, evidence-backed classification (what was found, why it was flagged, and what to do next) that holds up even when every other source is silent, so agents can close, escalate, or document the case on their own.
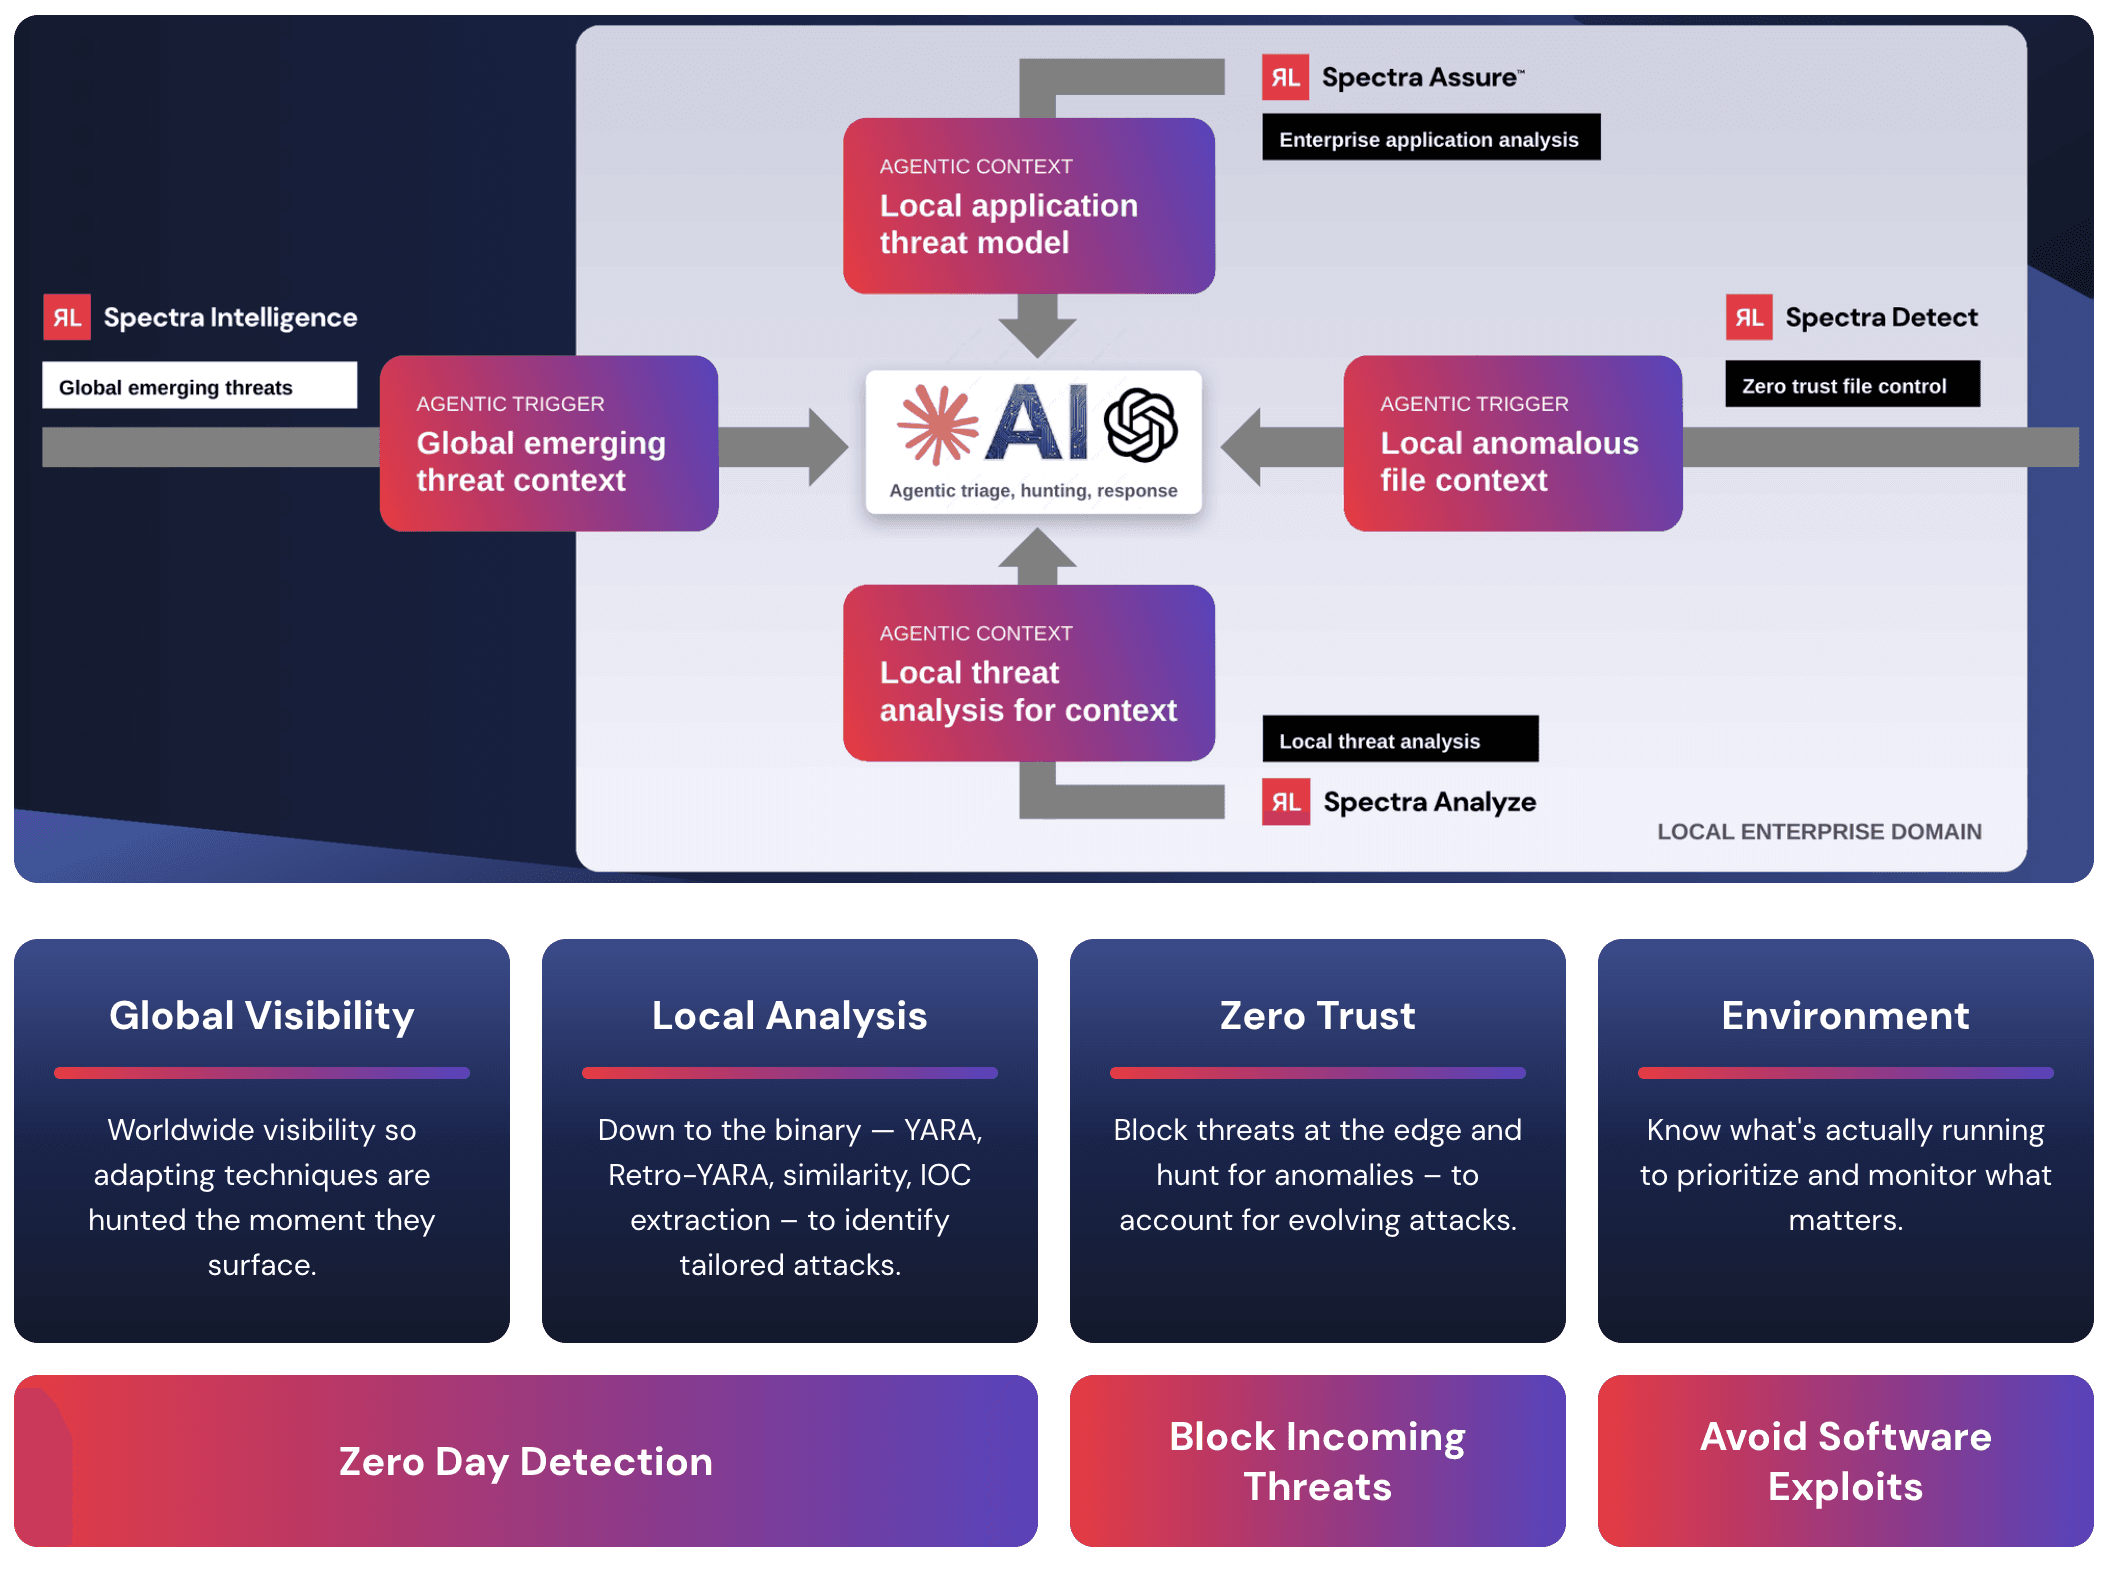
ReversingLabs' platform of products feed the agentic-workflow hub that handles triage, hunting, and response - grounding the AI-powered SOC in truth.
Cut manual validation from minutes to seconds with an independent, evidence-backed verdict on every indicator. Well-evidenced false positives close without analyst involvement, while true positives escalate with a pre-built, multi-source enrichment summary. Analysts redirect their time to high-impact investigation, hunting, and detection engineering.
New and novel threats make it difficult to get a confident classification when OSINT and other reputation sources are sparse, silent, or in conflict, creating a critical coverage gap. When one source reads “suspicious” and a sandbox reads “clean,” RL provides the vital independent threat context and acts as the tie-breaker that lets the agent conclusively resolve the case.
For confirmed threats, deep binary analysis tells the agent what the threat does, not just that it is malicious: persistence mechanisms, C2 infrastructure, dropped files, and capabilities such as encryption, data exfiltration, reconnaissance, and lateral movement. Responders know the impact and what to clean up before they open the case.
Give release and procurement agents a verdict that SCA can't. SCA checks what a package claims to contain; RL analyzes the complete final package (open source, commercial software, containers, and AI models) for malware, tampering, and hidden risk, so automated pass/fail decisions are defensible to customers and auditors.
Plug ReversingLabs into Claude, AWS Bedrock, LangChain, n8n, or custom orchestration with no heavy lift. Every verdict traces back to reproducible RL evidence in the case record, and resolved outcomes - including human overrides - become labeled training data and continuously improve downstream triage.
ReversingLabs is a founding member of the Agentic SOC Alliance, launched on July 22, 2026 by ExtraHop with 15 member companies, including CrowdStrike and LangChain.
ReversingLabs gives SOC teams and agentic workflows a proven advantage.
Deterministic, Evidence-Backed Verdicts
Binary, evidence-backed classifications eliminate the hallucination risk of ambiguous inputs feeding autonomous action. The same file, analyzed again, produces the same evidence, so agents and the analysts auditing them are never asked to trust an opaque confidence score. Where context is incomplete, RL says so rather than papering over it.
Industry's Largest Threat Intelligence Corpus
450 billion analyzed, searchable files, with millions of new samples analyzed every day, built first-party over more than a decade and not resold or aggregated from third parties. Real-time API lookups mean agents never act on a stale cache, and the depth to return an earlier, more detailed verdict exactly when community data goes quiet.
Full-Spectrum Analysis, One Trusted Source
Deep static and dynamic analysis deconstructs files and complete software packages down to the binary level, unpacking, de-obfuscating, and extracting embedded objects across the industry's broadest file-type coverage. One verdict source for files, network indicators, and software packages, instead of a stack of point tools.
Built for Agentic Pipelines, Not Bolted On
Purpose-built APIs, connectors, skills, agents, and MCP Servers, designed for agentic pipelines rather than a dashboard retrofitted after the fact. Designed to plug into the SIEM, SOAR, TIP, EDR, and XDR stack you already run. Validate it side by side: submit your own file population and compare verdicts against your current tooling.

ReversingLabs identified and classified the malware weeks before the report was published — showing why behavioral intelligence and historical telemetry matter in the AI age.

Discover how Command Zero and ReversingLabs integrate to speed SOC investigations, cut false positives, and deliver high‑fidelity cyber intelligence.