On-demand
Red Team vs. the Build Pipeline
RL Spectra Collective
Testing the defenses of the software supply chain has never been more essential — and developers themselves need to understand where the exploitable avenues lie. In this tactical demonstration, centered on the build pipeline itself, DevSecOps practitioners will see first-hand how these attacks actually unfold, and what best practices thwart them.
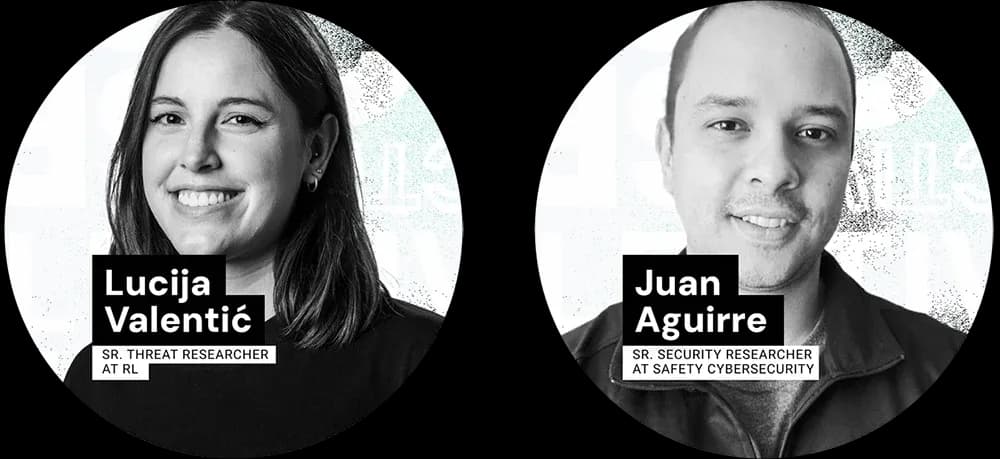
RL Community Manager Kadi McKean will be joined by Juan Aguirre, Sr. Security Researcher at Safety Cybersecurity, who will demonstrate how he would compromise a CI/CD pipeline or build system via stolen secrets, poisoned dependencies, misconfigured runners, and more. To flip back to the defensive perspective, Kadi will welcome RL Sr. Threat Researcher Lucija Valentić, who will walk through real-world cases built on these same techniques — including the infamous Shai-Hulud worm that cascaded across npm in late 2025.
In this session, DevSecOps practitioners and AppSec professionals will learn: